QuestionQ32

VerifiedAnalytics

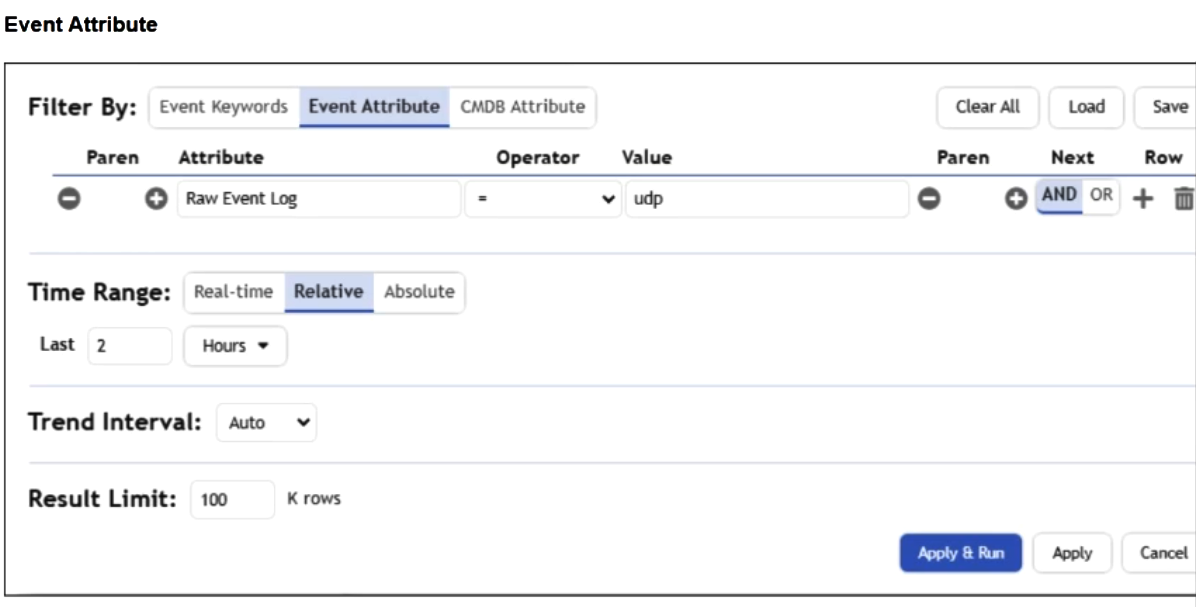
Refer to the exhibit.

Question Image

FortiSIEM is receiving syslog events from a firewall.

You are attempting to search raw event logs from the last two hours for traffic containing the keyword “UDP.” However, the search returns no results.

Based on the filter displayed in the exhibit, why are no search results returned?

Explanation

A raw event log is a string containing the full received message. Searching it for a keyword requires a pattern-matching operator such as CONTAIN; = tests for an exact equality match and therefore does not match normal raw log messages that merely include udp.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!