QuestionQ16

VerifiedTroubleshooting Wireless Networks

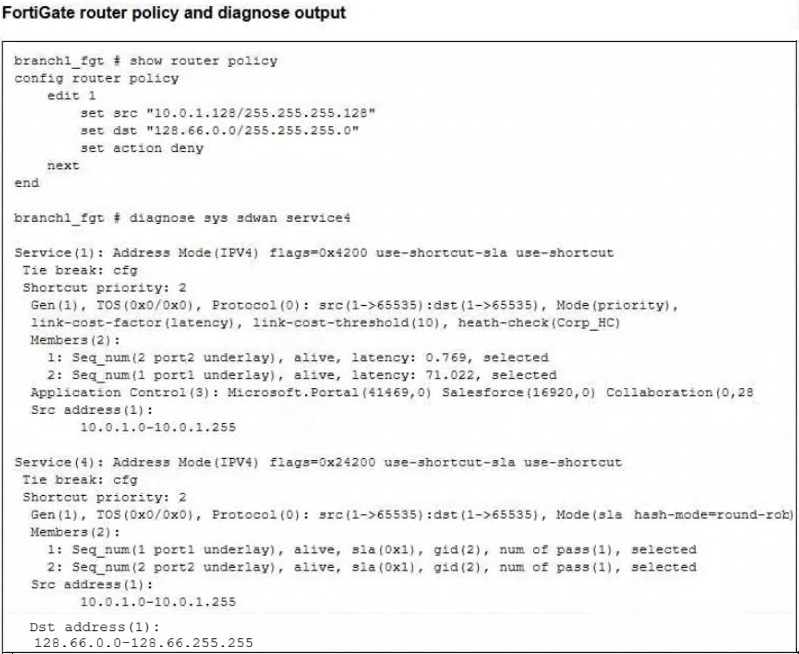
Refer to the exhibit.

Question Image

How does FortiGate process traffic with source IP 10.0.1.130 and destination IP 128.66.0.125?

Explanation

The traffic matches the router policy because both its source and destination addresses fall within the configured subnets. A router-policy action of deny means FortiGate does not search the policy-route table; it therefore uses the normal forwarding information base (FIB) routing decision rather than applying the SD-WAN service rule or dropping the traffic.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!