QuestionQ49
VerifiedDeployment and configurationRefer to the exhibits.
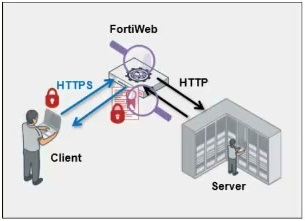
You are setting up SSL offloading on FortiWeb to secure a public-facing application. Clients connect over HTTPS, and FortiWeb forwards requests to the back-end server over HTTP.
You are reviewing certificate deployment and must determine where to install the private key for the certificate used for client connections.
In this SSL-offloading configuration, which device uses the private key associated with the web server certificate?
Community Discussion