QuestionQ45
VerifiedCompliance and troubleshootingRefer to the exhibits.
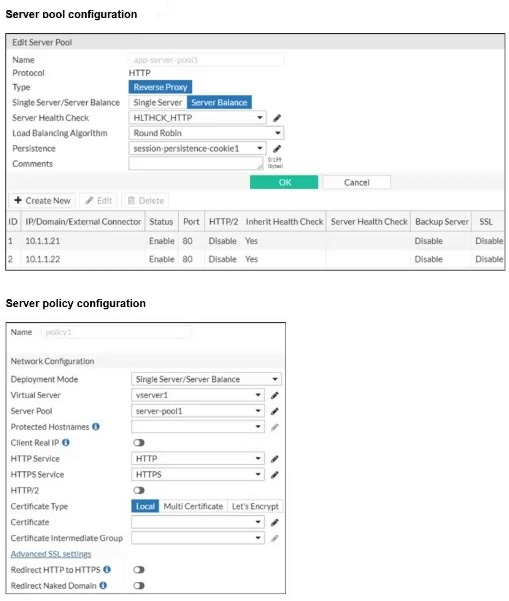
You are configuring a FortiWeb appliance in reverse proxy mode, located downstream from a FortiGate. The server pool contains two back-end web servers, 10.1.1.21 and 10.1.1.22, and you have configured a health-check policy.
After you complete the server-policy configuration and apply it to a virtual server, FortiWeb does not forward traffic to the back-end servers. The logs show no errors or health-check failures.
Based on the configuration in the exhibit, what change should you make to restore back-end traffic flow?
Community Discussion