QuestionQ123

VerifiedUnderstanding Cyber Threats, IoCs, and Attack Methodology

An attacker attempting to exploit the vulnerability in the dynamically generated welcome page appended the following code to the end of the company’s URL:
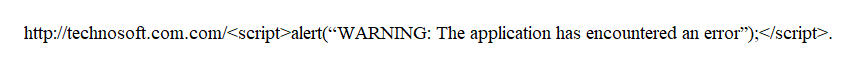
Question Image

Identify the attack shown in this scenario.

Explanation

Cross-site scripting (XSS) injects malicious client-side script into a web page so that it executes in a victim’s browser. The appended <script> payload and JavaScript alert() are characteristic of an XSS attack.

Community Discussion

No comments yet. Be the first to start the discussion!