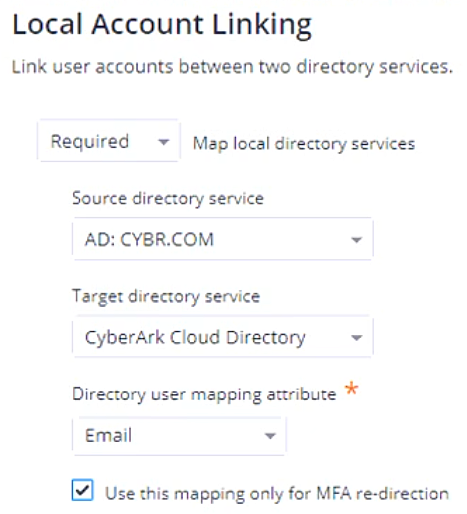
QuestionQ52Verified/Advanced WorkflowsCopy linkReport a problemAsk AstroTutorSave questionRefer to the exhibit. If an Authentication Policy is configured as shown, which statement is correct? AThe Initial MFA challenge will be sent to the account in CyberArk Cloud Directory (Target).BUpon successful logon, the user will be logged in as the account in CyberArk Cloud Directory (Target).CFuture MFA challenges will be sent to the account in AD (Source).DIf there is no matching email between two accounts in AD (Source) and CyberArk Cloud Directory (Target), the mapping will then look for a matching User ID.Show AnswerAnswerExplanationWhen local account linking is configured only for MFA re-direction, CyberArk redirects MFA challenges to devices associated with the target-directory user while the user signs in as the source-directory user. With AD: CYBR.COM as the source and CyberArk Cloud Directory as the target, the initial MFA challenge is sent to the target account. Required linking requires a matching account and does not fall back from Email to User ID.Learn moreCyberArk: Link identities across directories for consistent sign-in and accessShow comments0Show commentsCommunity DiscussionNo comments yet. Be the first to start the discussion!
Community Discussion