QuestionQ60
VerifiedLayer 2 VPNsRefer to the exhibit.
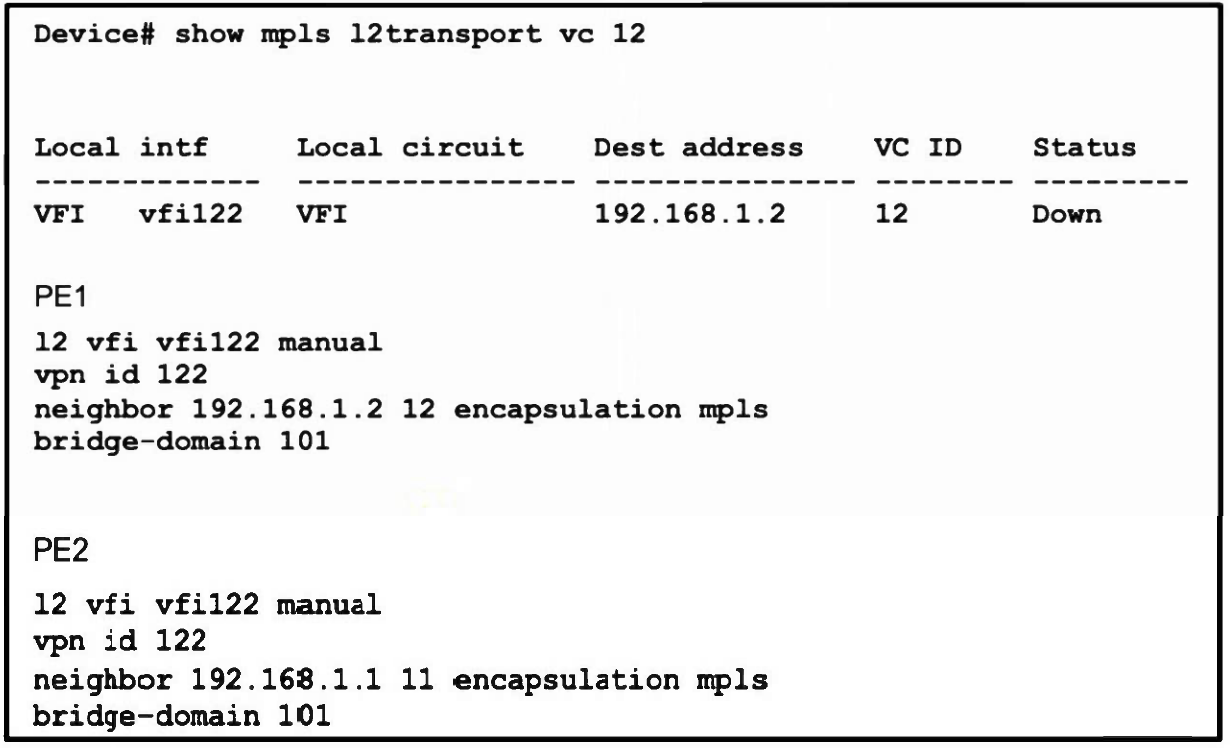
A customer connected to a service provider is operating VPLS. Client applications need Layer 2 extended between sites. However, the customer’s security team wants to prevent Layer 3 routing from being shared with the service provider. A service-provider engineer configured PE1 and PE2 as shown to support the customer’s traffic requirements, but the circuit is down. What action must the engineer take to resolve the issue?
Community Discussion