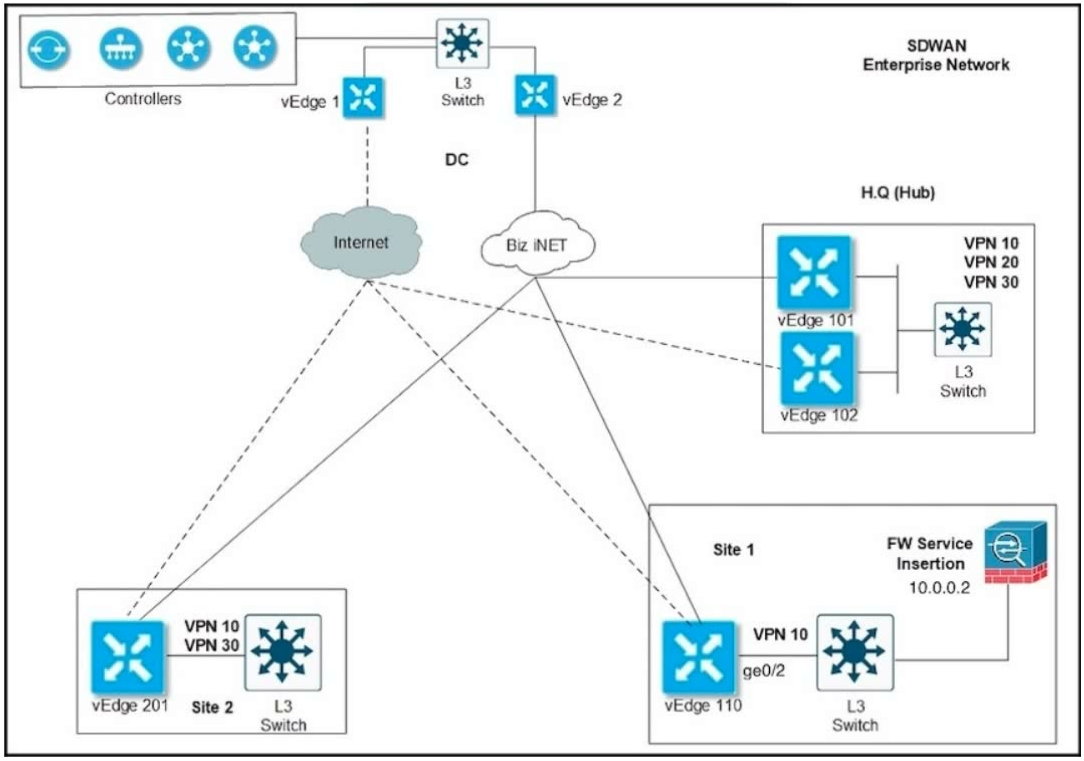
Service insertion in Cisco SD-WAN is implemented on the vSmart controller with a centralized control policy: routes of the service VPN are matched and the accept action sets the advertised network service, so vSmart rewrites the VPN 10 routes it advertises and traffic from the receiving sites is drawn through the firewall service registered at the service site. Matching VPN 10 routes and setting the service accomplishes this requirement. A data policy that sets an IP next hop cannot steer remote-site traffic into a firewall at another site, because a next-hop address must be locally reachable from the ingress router, and TLOC-steering actions forward to a transport locator without invoking any registered service.
Community Discussion