QuestionQ48

VerifiedSecurity and Quality of Service
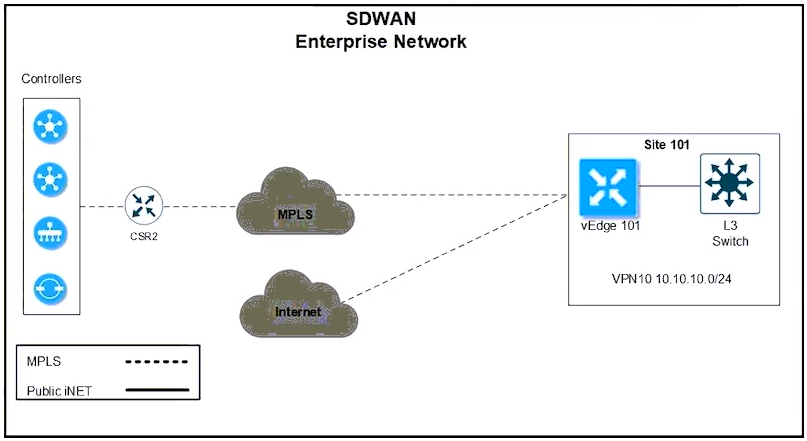
Question Image

Drag the code snippets shown below into the configuration boxes to stop ICMP packets from the internet circuit from reaching VPN10 users at site 101. Some options will not be used.

Scope: This is a data-policy-body exercise. List definitions, policy application, and activation are outside the fragment.

Drag & Drop
data-policy VPN10_Data_Policy
  vpn-list VPN10
    sequence 1
      match
        
        destination-ip 10.10.10.0/24
      action 
    default-action 
Explanation

The protected VPN10 subnet is the packet destination, so the sequence matches destination-ip 10.10.10.0/24. IPv4 ICMP uses protocol 1; protocol 58 is ICMPv6 and protocol 2 is IGMP. For traffic evaluated by this policy body, drop discards matching packets and default-action accept permits nonmatching packets. The default action belongs inside vpn-list, at the same level as sequence.

The body does not select an ingress circuit. Policy application and activation are separate, so this fragment alone does not establish Internet-only enforcement or an MPLS exemption.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!