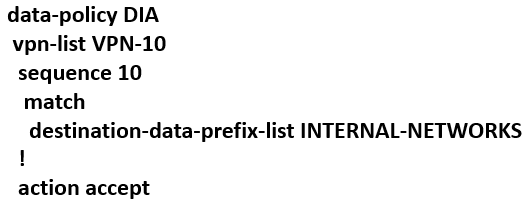
An engineer configures this DIA data policy for VPN 10:
Which policy sequence enables DIA for external networks?
DIA traffic must be accepted and directed to the NAT/DIA path (VPN 0). A destination match of 0.0.0.0/0 serves as the catch-all for external destinations. Placing that rule after the INTERNAL-NETWORKS destination exception preserves normal handling for internal traffic; an earlier source-based 0.0.0.0/0 rule would match all traffic first. Cisco documents nat use-vpn 0 as the action that directs matching traffic to the NAT functionality for Internet/DIA access.
0.0.0.0/0
INTERNAL-NETWORKS
nat use-vpn 0
Community Discussion