QuestionQ57
VerifiedThreat Hunting TechniquesRefer to the exhibit.
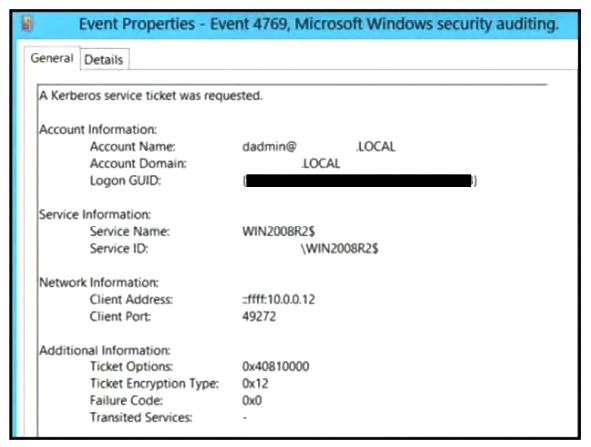
A company’s security team reviews Intrusion Prevention System logs and identifies a pass-the-hash attack against a domain controller. Further investigation finds that the attack originated from an endpoint running the Mimikatz tool. The team must increase visibility into the company’s endpoint actions and add further logging to detect similar attacks in the future.
Which logs should the team use?
Community Discussion