300-220 CBRTHD: Conducting Threat Hunting and Defending using Cisco Technologies for Cybersecurity
By Cisco · Question Mode
QuestionQ52
Threat Hunting Outcomes
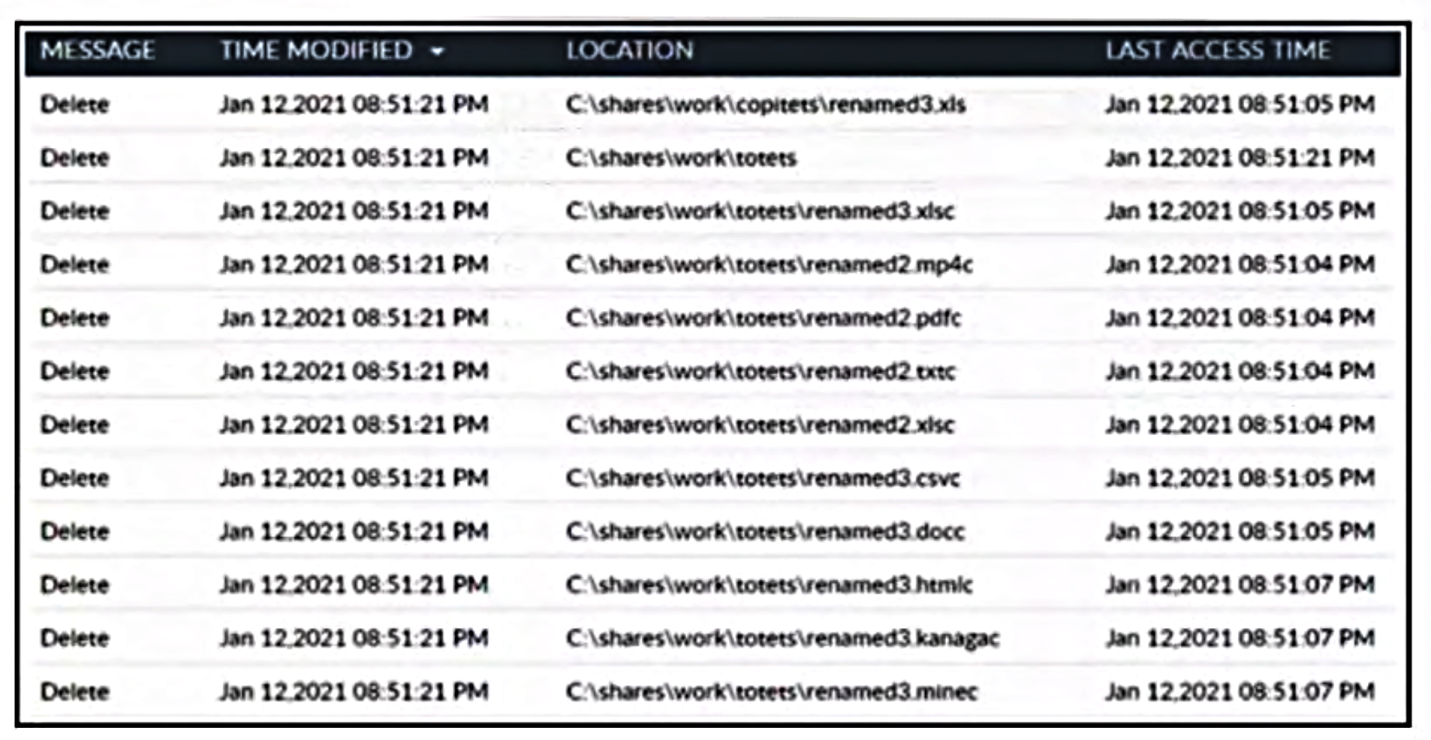
Refer to the exhibit.
A cybersecurity team receives an Intrusion Prevention System alert about multiple file changes on a file server. Before those changes, the team detected a successful remote sign-in to the server from a user account.
Which type of threat occurred?
Community Discussion
No comments yet. Be the first to start the discussion!
Community Discussion