300-220 CBRTHD: Conducting Threat Hunting and Defending using Cisco Technologies for Cybersecurity
By Cisco · Question Mode
QuestionQ50
Threat Hunting Outcomes
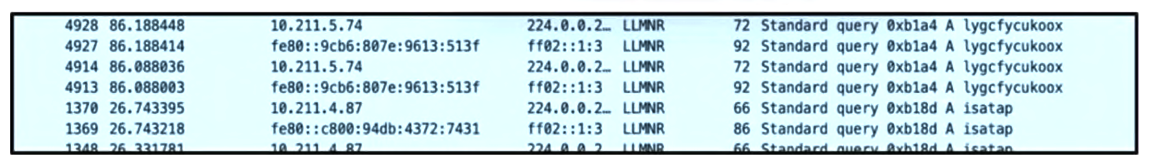
Refer to the exhibit.
A security engineer uses Wireshark to observe Link-Local Multicast Name Resolution (LLMNR) and NetBIOS Name Service traffic that could spoof a name-resolution source, forcing communication with an adversary-controlled system and enabling an SMB Relay attack. After identifying the traffic as malicious, the security engineer must determine the gaps in threat detection.
Which gap would an analyst identify?
Community Discussion
No comments yet. Be the first to start the discussion!
Community Discussion