QuestionQ43
Threat Hunting TechniquesRefer to the exhibit.
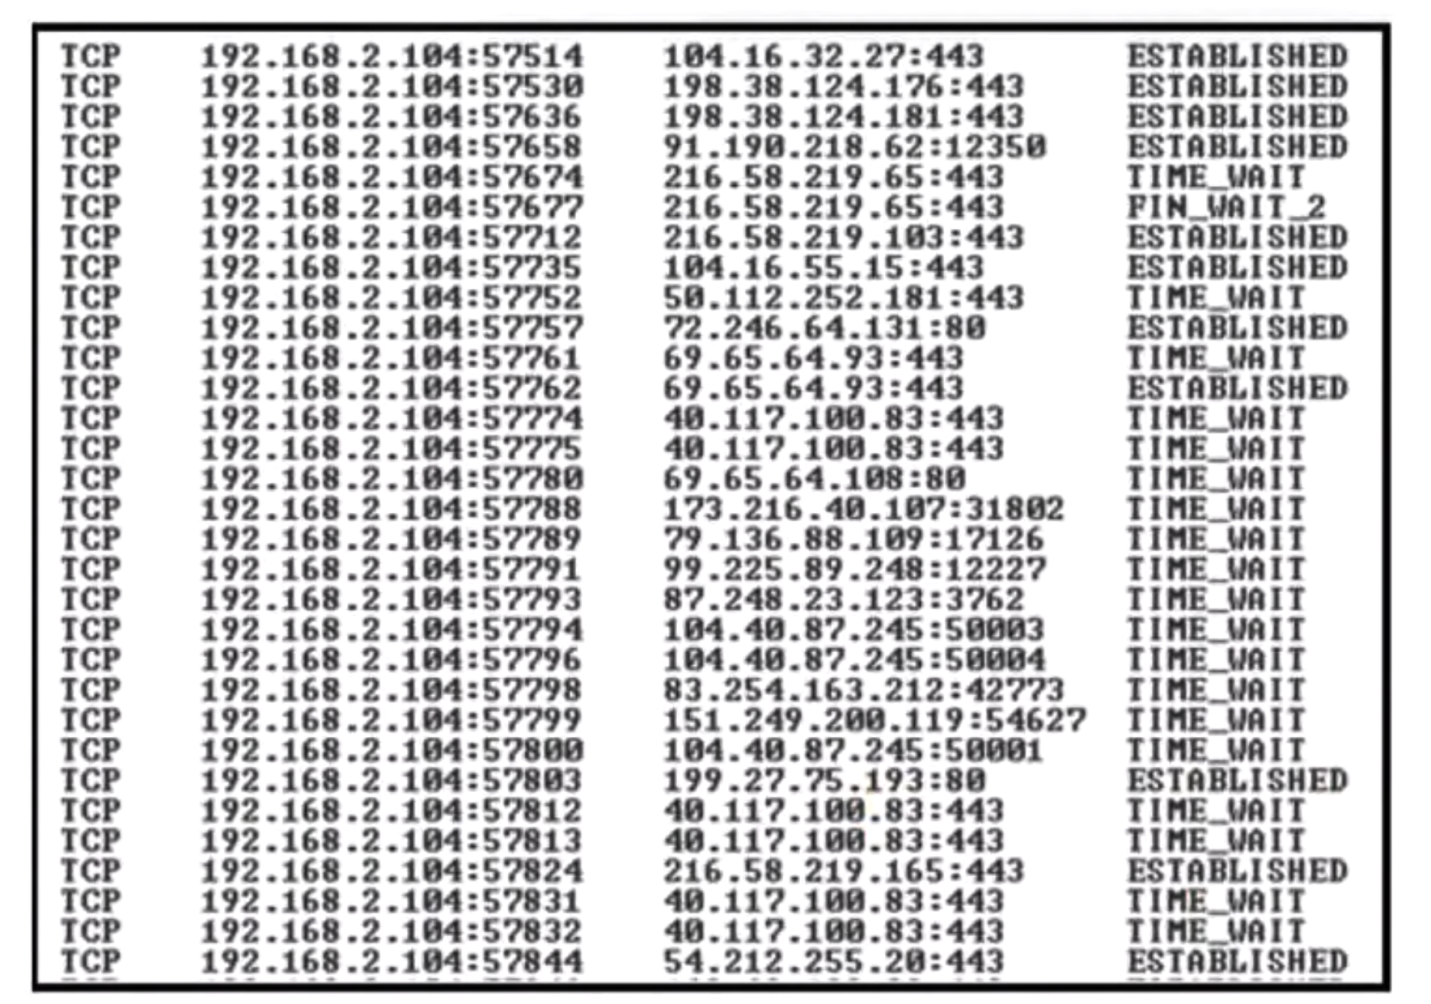
A security team detects a traffic spike originating from the company web server. After further investigation, the team finds that the server has established multiple connections to different IP addresses, but the web server logs include both expected traffic and DDoS traffic.
Which attribute must the team use to further filter the logs?
Community Discussion