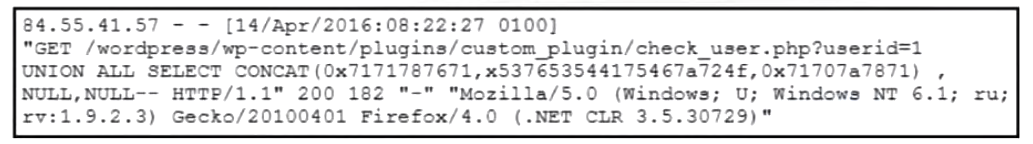
Refer to the exhibit.
A forensic team needs to investigate how the company website was defaced. The team isolates the web server, clones the disk, and examines the logs.
Which technique did the attacker initially use to access the website?
The request places UNION ALL SELECT SQL syntax into the userid parameter of a public WordPress plugin endpoint, indicating SQL injection. Exploiting this weakness in an Internet-facing web application for initial access is MITRE ATT&CK technique T1190, Exploit Public-Facing Application.
UNION ALL SELECT
userid
Community Discussion