300-220 CBRTHD: Conducting Threat Hunting and Defending using Cisco Technologies for Cybersecurity
By Cisco · Question Mode
QuestionQ30
Threat Hunting Processes
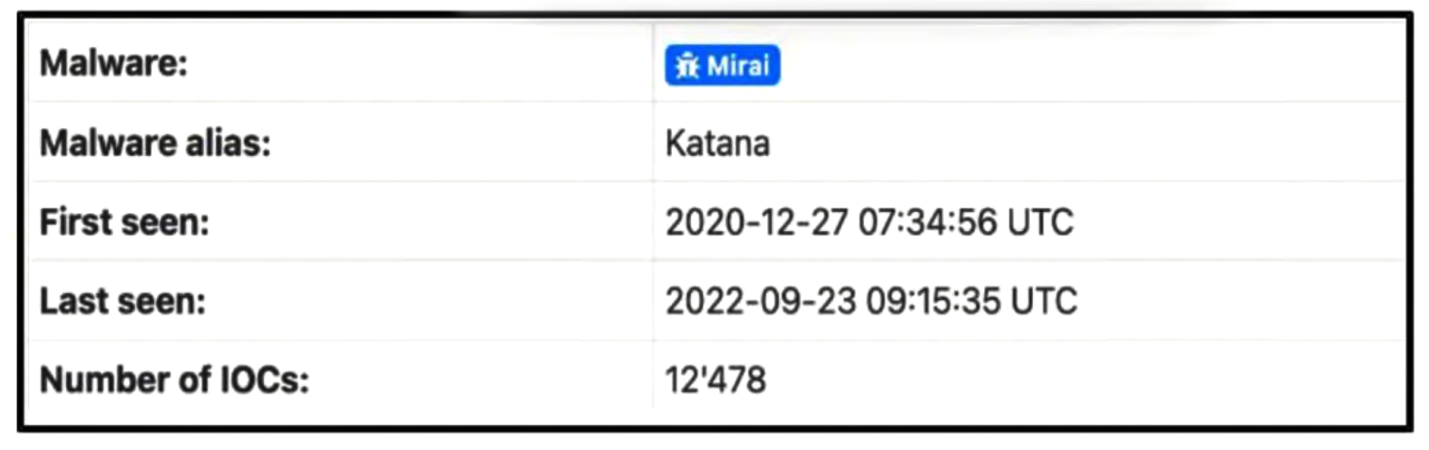
Refer to the exhibit.
A threat analyst examines an OSINT platform used to share and request indicators of compromise associated with various malware strains. The analyst must obtain threat intelligence from the platform about the indicators of compromise for future intelligence-driven threat hunting.
Which action should the analyst take to achieve this goal?
Community Discussion
No comments yet. Be the first to start the discussion!
Community Discussion