300-220 CBRTHD: Conducting Threat Hunting and Defending using Cisco Technologies for Cybersecurity
By Cisco · Question Mode
QuestionQ28
Threat Hunting Processes
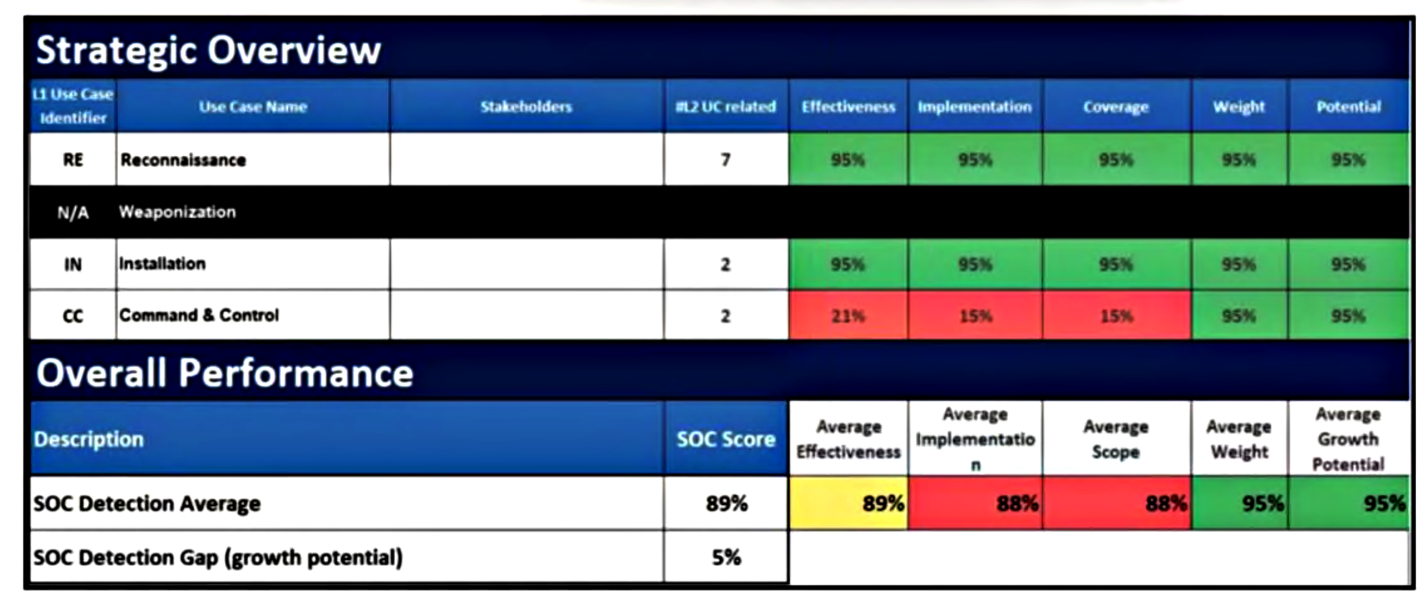
Refer to the exhibit.
An organization engages a Breach and Attack Simulation vendor to measure response readiness and identify threat-detection coverage gaps within its SOC capability. The organization also uses the TaHiTI Magma Threat Hunting methodology and its Use Case Framework for the case-management lifecycle and to define detection technology and log sources across the organization. The organization must keep threat-detection coverage current.
Which gaps would an analyst diagnose from the exhibit?
Community Discussion
No comments yet. Be the first to start the discussion!
Community Discussion