QuestionQ22
Threat Hunting TechniquesRefer to the exhibit.
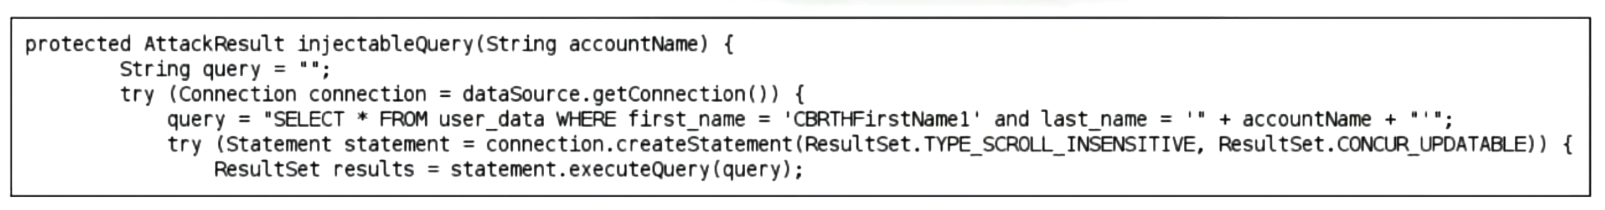
Code analysis is performed using the Semgrep tool. The tool reports that a security issue occurred while connecting to the database.
Which security vulnerability does the tool flag?
Refer to the exhibit.
Code analysis is performed using the Semgrep tool. The tool reports that a security issue occurred while connecting to the database.
Which security vulnerability does the tool flag?
Community Discussion