QuestionQ18
VerifiedThreat Hunting TechniquesRefer to the exhibit.
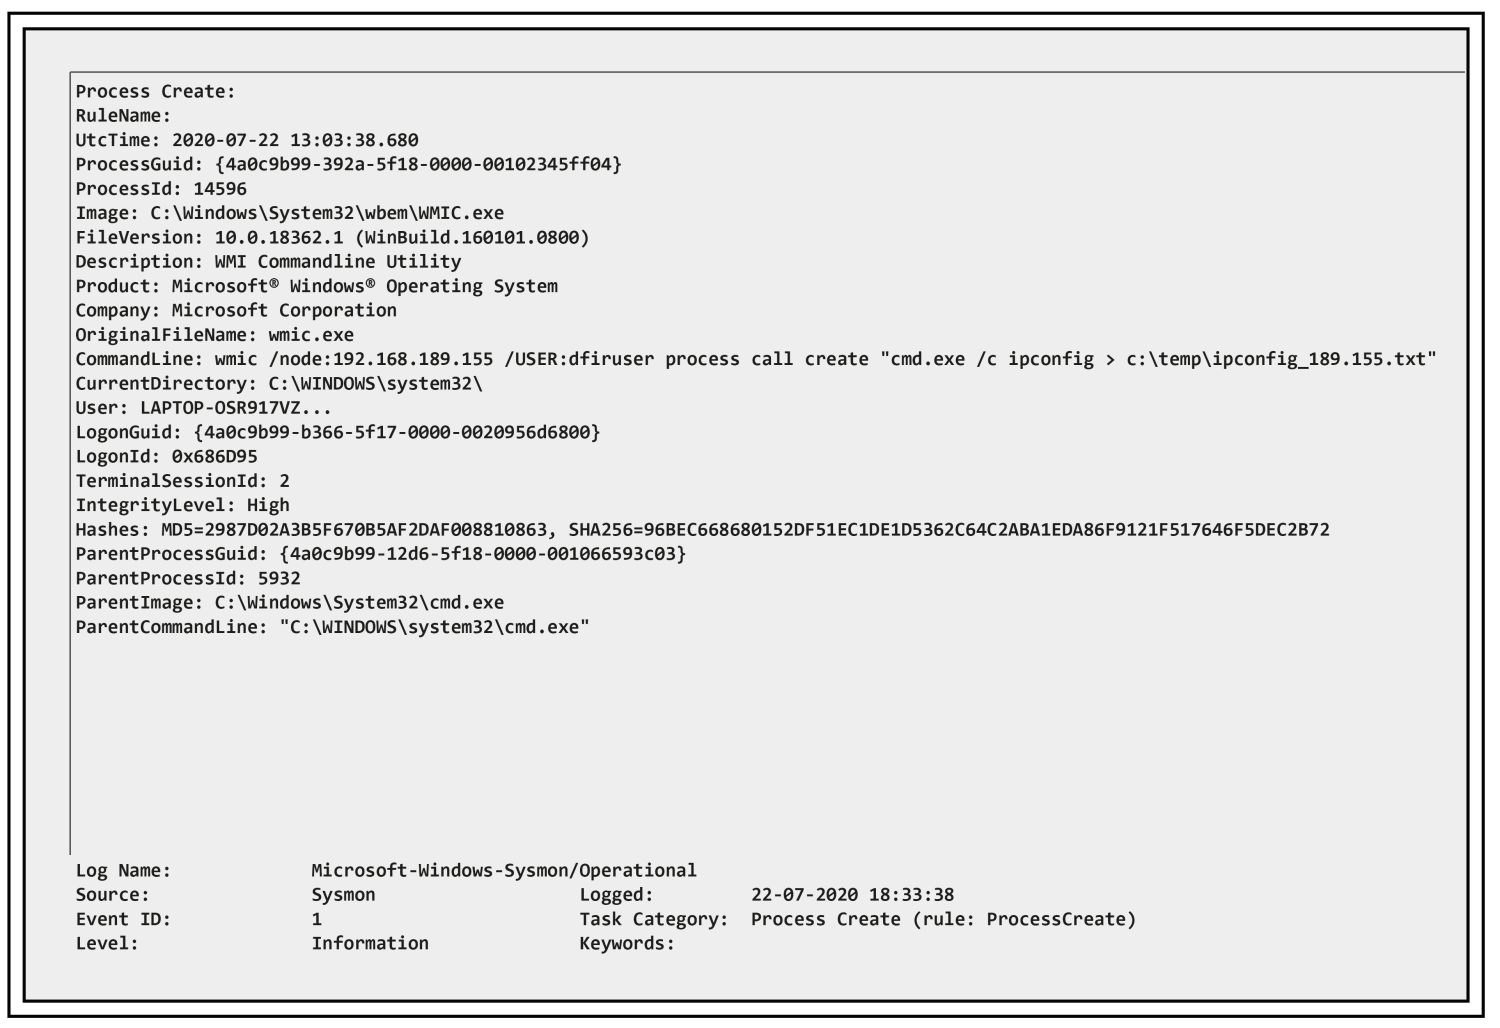
After receiving an alert that a Windows host authenticated over the network to another host using a local administrator account, the security team examines the host. The team finds a process-creation event in that host's Sysmon logs.
Which action did the host carry out?
Community Discussion