300-220 CBRTHD: Conducting Threat Hunting and Defending using Cisco Technologies for Cybersecurity
By Cisco · Question Mode
QuestionQ13
Threat Hunting Techniques
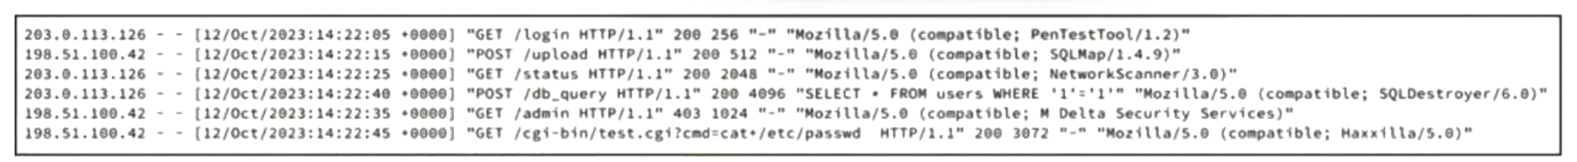
Refer to the exhibit.
The SOC lead received the scope for a penetration test performed against the company's assets during the last 4 hours. The documentation does not appear to include an authorized IP address range, and the testing company may perform only a surface-level scan and database probing. While SOC analysts review server logs to determine whether recent activity indicates an authorized penetration test or a possible attack, the team discovers several suspicious entries.
Which two log entries indicate a potentially successful unauthorized attack?
Choose two
Community Discussion
No comments yet. Be the first to start the discussion!
Community Discussion