QuestionQ11
VerifiedThreat Hunting TechniquesRefer to the exhibit.
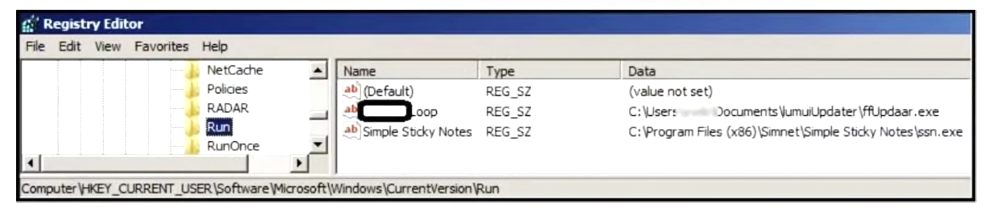
An analyst is evaluating artifacts and logs collected from a recent breach. In the logs, ATP established malware persistence by placing a path to the executable in a specific registry entry.
What distinguishes the ATP’s approach from using HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\Run instead?
Community Discussion