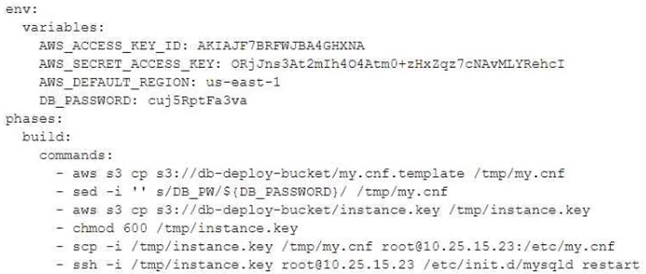
A DevOps engineer is working on a project hosted on Amazon Linux that has failed a security review. The DevOps manager has been asked to review the company’s buildspec.yaml file for an AWS CodeBuild project and make recommendations. The buildspec.yaml file is configured as follows:
Which changes should be recommended to comply with AWS security best practices?
Choose three
Community Discussion
No comments yet. Be the first to start the discussion!
Community Discussion