QuestionQ62
VerifiedContinuous Improvement for Existing SolutionsA company with several AWS accounts uses AWS Organizations and service control policies (SCPs). An administrator created the following SCP and attached it to an organizational unit (OU) that contains AWS account 1111-1111-1111:
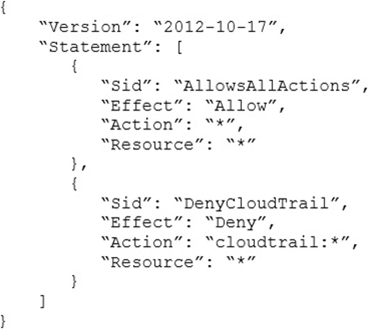
Developers in account 1111-1111-1111 report that they cannot create Amazon S3 buckets. How should the administrator resolve this problem?
Community Discussion